

Description
Sophos XGS 3300

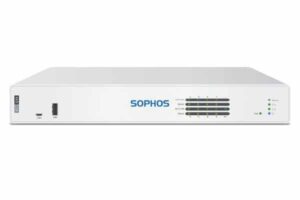
The Sophos XGS 3300 is a 1U next-generation firewall designed for organizations requiring high-performance security and flexible network connectivity. It combines Sophos Firewall software capabilities with dedicated hardware acceleration designed to improve performance for qualifying firewall and IPsec traffic.
With up to 58 Gbps firewall throughput, 14 Gbps IPS throughput, 10 Gbps Threat Protection throughput, and 12.5 Gbps NGFW throughput, the XGS 3300 provides a platform for demanding enterprise and distributed-edge environments.
Connectivity
The XGS 3300 includes eight Gigabit Ethernet copper ports, two SFP fiber interfaces, and two SFP+ 10GbE fiber interfaces. One of the copper port pairs supports bypass functionality. The appliance also includes dedicated management and console interfaces.
The integrated SFP+ interfaces allow the firewall to participate in higher-speed network connections, while the copper ports support conventional Gigabit Ethernet deployments.
Flexi Port Expansion
A key feature of the XGS 3300 is its single Flexi Port expansion slot. Compatible Flexi Port modules can add additional copper or fiber interfaces and can provide options such as 10GbE SFP+, PoE, and other supported port configurations.
Organizations should confirm the exact Flexi Port module, hardware revision, transceiver requirements, and supported configuration before ordering.
Security and Performance
The XGS 3300 is designed to handle firewall, IPS, threat protection, VPN, and SSL/TLS inspection workloads. Sophos publishes up to 13.7 million concurrent connections and 257,800 new connections per second for the platform.
Its Xstream architecture uses dedicated processing hardware to accelerate qualifying firewall and IPsec traffic. Sophos describes this architecture as offloading appropriate workloads to the Xstream Flow Processor and associated acceleration hardware.
VPN Capabilities
The XGS 3300 supports IPsec VPN throughput of up to 31.1 Gbps and up to 6,500 concurrent IPsec VPN tunnels. It also supports up to 5,000 concurrent SSL VPN tunnels. These capabilities make the platform suitable for organizations connecting offices, users, and remote environments securely.
Rackmount Deployment
The XGS 3300 uses a 1U chassis measuring 438 × 44 × 405 mm and weighing approximately 4.7 kg when unpacked. It includes rackmount ears for installation in standard rack environments.
The appliance includes an internal auto-ranging AC-DC power supply and supports an external redundant power supply option.
Why Choose Sophos XGS 3300?
The XGS 3300 brings together high-speed firewall processing, integrated 10GbE connectivity, flexible port expansion, VPN capabilities, and a rack-ready form factor. It is suited to organizations that require a scalable firewall platform while retaining flexibility in network interface selection.
Selection Guide
For High-Speed Firewall Deployment
Review expected internet, WAN, LAN, and inter-network traffic requirements. The XGS 3300 publishes up to 58 Gbps firewall throughput and 12.5 Gbps NGFW throughput.
For 10GbE Connectivity
Use the integrated SFP+ interfaces for supported 10GbE fiber connections. Select compatible Sophos or approved transceivers based on the required fiber type, distance, and network equipment.
For Additional Ports
Review the available Flexi Port modules and select the appropriate module based on copper, fiber, 10GbE, PoE, or other connectivity requirements. Sophos lists multiple supported module configurations for the XGS 3300.
For VPN Deployments
Consider the number of expected site-to-site and remote VPN connections. The published XGS 3300 specification supports up to 31.1 Gbps IPsec VPN throughput and 6,500 concurrent IPsec VPN tunnels.
For Redundant Power
If power redundancy is required, verify the availability and compatibility of the external redundant PSU option before purchase.
Always Verify
Check the latest Sophos product documentation, hardware revision, supported Flexi Port modules, transceiver compatibility, and licensing requirements before purchasing.
Installation Notes
The Sophos XGS 3300 is designed for 1U rack installation. Install the supplied rackmount hardware according to Sophos’ hardware instructions and provide adequate clearance and airflow around the appliance.
Connect the required WAN, LAN, SFP, or SFP+ interfaces according to the network design. Use compatible transceivers and appropriate fiber or copper cabling for each interface.
When installing a Flexi Port module, follow the relevant Sophos hardware installation instructions and verify that the module is supported by the specific XGS 3300 hardware revision.
For high-speed SFP+ connections, verify that the selected transceivers and connected devices use compatible speed and interface settings. Sophos notes that Flexi Port configurations on XGS 2100, 2300, 3100, and 3300 appliances have specific speed-configuration requirements for SFP+ ports.
Best Practices
- Install the XGS 3300 in an appropriate 1U rack position.
- Maintain adequate airflow around the appliance.
- Use compatible Sophos or listed transceivers.
- Verify Flexi Port compatibility before installation.
- Label WAN, LAN, SFP, and SFP+ connections.
- Document all installed expansion modules and transceivers.
- Plan 10GbE links according to actual bandwidth requirements.
- Keep Sophos Firewall firmware up to date.
- Use appropriate VPN and security policies for remote connectivity.
- Verify redundant power requirements before deployment.
- Maintain current network diagrams and firewall configuration documentation.
- Confirm hardware and firmware requirements before deploying high-availability configurations.
Sophos documents that hardware appliances used in HA must use the same firewall model, and Flexi Port configurations must match between HA devices where modules are installed.
Benefits for IT Teams
- High-capacity firewall platform for demanding environments.
- Integrated 10GbE connectivity reduces the need for additional interface hardware.
- Flexible expansion supports changing connectivity requirements.
- 1U rack design simplifies structured deployment.
- High connection capacity supports large user and application environments.
- Strong VPN throughput supports distributed organizations.
- Centralized Sophos management can simplify firewall administration.
- Model-specific hardware and expansion options provide a clearer support path.
- Optional redundant power supports deployments where power resilience is required.
Main Benefits
High-Speed Network Security
Benefit: Up to 58 Gbps firewall throughput provides substantial processing capacity for high-traffic networks.
Advanced Threat Inspection
Benefit: Published IPS and Threat Protection performance supports security inspection across enterprise network traffic.
Flexible Connectivity
Benefit: Built-in copper, SFP, and SFP+ interfaces provide options for different network media and speeds.
Expandable Port Density
Benefit: One Flexi Port slot can increase interface density or introduce additional supported connectivity options.
Strong VPN Capacity
Benefit: Up to 31.1 Gbps IPsec VPN throughput and 6,500 concurrent IPsec tunnels support secure site-to-site and remote connectivity.
Rack-Ready Deployment
Benefit: The 1U chassis fits standard rack environments and helps organizations integrate firewall security into structured network infrastructure.
Typical Use Cases
1. Enterprise Network Security
Deploy the XGS 3300 at the network edge to inspect and control traffic between internal networks, the internet, remote locations, and other network zones.
2. Campus Networks
Use the firewall to provide centralized security for organizations with multiple departments, users, applications, and network segments.
3. High-Speed Internet Gateway
The combination of high firewall throughput and 10GbE interfaces makes the XGS 3300 suitable for environments requiring high-capacity internet or core network connectivity.
4. Site-to-Site VPN
Use IPsec VPN capabilities to securely connect branch offices, remote sites, data centers, and other business locations. The platform supports up to 6,500 concurrent IPsec VPN tunnels.
5. 10GbE Network Integration
Connect the firewall to 10GbE-capable switches, servers, or other network infrastructure using its integrated SFP+ interfaces.
6. Expandable Network Deployments
Use compatible Flexi Port modules when the fixed interface configuration does not provide the required number or type of ports.
7. Distributed Edge Security
Deploy the XGS 3300 as part of a distributed network security architecture where multiple sites and network segments require centrally managed firewall protection.
Who Should Buy Sophos XGS 3300?
The Sophos XGS 3300 is intended for organizations that require a high-performance 1U next-generation firewall with 10GbE connectivity and expandable interfaces.
It can be considered for:
- Medium and large enterprises
- Campus networks
- Distributed organizations
- Data-center edge deployments
- Branch aggregation environments
- Managed service providers
- Organizations requiring high-capacity VPN connectivity
- Networks integrating 10GbE infrastructure
The appropriate model should be selected based on traffic levels, security inspection requirements, VPN demand, port requirements, and future expansion plans.
Related Categories
Explore related Sophos products and categories:
- Sophos Firewalls
- Sophos XGS Series
- Sophos XGS 3100
- Sophos XGS 2300
- Sophos XGS 2100
- Sophos Flexi Port Modules
- Sophos SFP and SFP+ Transceivers
- Sophos Firewall Accessories
- Sophos Firewall Licenses
- Sophos Rackmount Solutions
Frequently Asked Questions
What is Sophos XGS 3300?
The Sophos XGS 3300 is a 1U next-generation firewall designed for enterprise and distributed-edge network security. It provides integrated copper, SFP, and SFP+ interfaces with one Flexi Port expansion slot.
What is the firewall throughput of Sophos XGS 3300?
The current Sophos technical specifications list firewall throughput of up to 58 Gbps for the XGS 3300.
What is the NGFW throughput of XGS 3300?
Sophos lists up to 12.5 Gbps NGFW throughput for the XGS 3300.
Does Sophos XGS 3300 support 10GbE?
Yes. The XGS 3300 includes 2 × SFP+ 10GbE fiber interfaces.
How many ports does the Sophos XGS 3300 have?
The fixed interfaces include 8 × Gigabit Ethernet copper, 2 × SFP fiber, and 2 × SFP+ 10GbE fiber ports. One Flexi Port slot can expand the interface configuration, with a maximum total port density of 20 according to Sophos documentation.
Does XGS 3300 support Flexi Port modules?
Yes. The XGS 3300 has one Flexi Port expansion slot and supports several optional module configurations, including copper, fiber, 10GbE SFP+, and PoE options.
What is the IPsec VPN throughput of XGS 3300?
Sophos publishes up to 31.1 Gbps IPsec VPN throughput and up to 6,500 concurrent IPsec VPN tunnels for the XGS 3300.
How many concurrent connections does XGS 3300 support?
The XGS 3300 supports up to 13.7 million concurrent connections and up to 257,800 new connections per second according to Sophos’ published specifications.
Is Sophos XGS 3300 rackmountable?
Yes. The XGS 3300 is a 1U rackmount firewall and includes rackmount ears.
Does XGS 3300 support redundant power?
The appliance has an internal auto-ranging AC-DC power supply and supports an optional external redundant power supply.
What storage does Sophos XGS 3300 have?
The XGS 3300 includes an integrated SATA-III SSD with a minimum capacity of 240 GB, used for local quarantine and logs.
Can Sophos XGS 3300 be used in high availability?
Sophos supports HA on XGS Series firewalls subject to its documented requirements. HA devices must use the same firewall model, and installed Flexi Port configurations must match between the devices.
Does XGS 3300 support Sophos Central Zero Touch?
Yes. Sophos lists the XGS 3300 among supported XGS models for Zero Touch deployment, subject to the documented serial-number and firmware requirements.


Reviews
There are no reviews yet.