
Description
BIG-IP SSL Orchestrator
SSL/TLS encryption protects data as it moves throughout networks; however, it could also create security blind spots while inspection tools can not see what’s inside encrypted traffic. Organizations using multiple security tools need a way to decrypt relevant traffic, make it available for inspection, and control how it moves through the security stack.
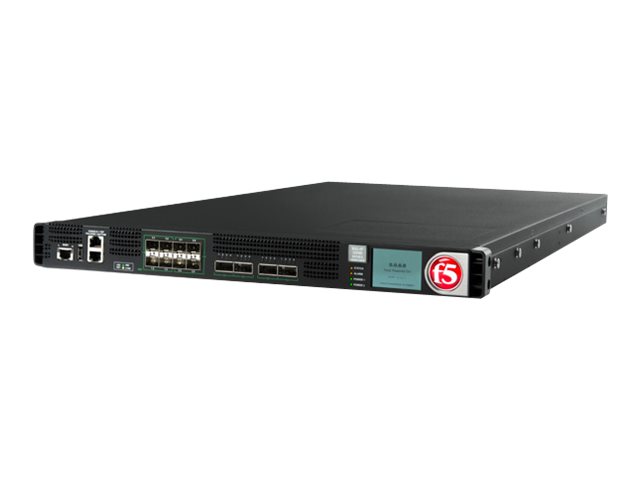
F5 BIG-IP SSL Orchestrator provides SSL/TLS visibility via decryption and re-encryption whilst dynamically directing traffic across protection inspection services. It supports policy-based traffic steering and service chaining, supporting businesses in using existing security investments more successfully.
Business Challenges
Organizations increasingly depend on SSL/TLS encryption for internet applications, cloud services, APIs, and user communications. While encryption protects data in transit, it can also prevent security tools from inspecting malicious content hidden within encrypted traffic.
Security groups may also use numerous inspection technologies, such as firewalls, intrusion prevention systems, DLP platforms, and other security managers. Manually connecting those tools can create complex traffic paths and make it difficult to determine which traffic should bypass which inspection service.
Why BIG-IP SSL Orchestrator Matters
BIG-IP SSL Orchestrator helps organizations make encrypted traffic visible to security inspection technologies whilst keeping control over how that traffic moves through the network. It combines SSL/TLS decryption and re-encryption with policy-based traffic steering and dynamic service chaining.
This technique is useful for organizations with multiple protection services that want access to encrypted traffic. Instead of manually creating fixed inspection paths, groups can use guidelines and context to determine how traffic needs to be treated. F5 additionally provides service monitoring and load-balancing abilities to guide the provision of security inspection offerings.
Key Features of BIG-IP SSL Orchestrator
SSL/TLS Visibility and Decryption
BIG-IP SSL Orchestrator decrypts and re-encrypts SSL/TLS traffic so security inspection services can inspect encrypted sessions. F5 identifies each inbound and outbound traffic flow as a data center, assisting organizations in inspecting traffic that would, in any other case, continue to be hidden from security tools.
Dynamic Service Chaining
Dynamic service chaining creates logical inspection paths that direct traffic through selected security services. Organizations can build different chains based on traffic’ needs in preference to sending every connection through the same series of security devices.
Policy-Based Traffic Steering
Policy-based traffic steering permits organizations to classify, inspect, and direct traffic consistent with defined conditions. F5 describes the functionality as the use of context-based intelligence across different network topologies, protocols, and ciphers to manage encrypted traffic flows.
Context-Based Intelligence
BIG-IP SSL Orchestrator can use contextual information while making traffic-handling decisions. F5 lists capabilities such as geolocation, IP reputation, URL categorization, and third-party ICAP integration, allowing corporations to use custom policies for different types of traffic.
Security Service Resiliency
SSL Orchestrator provides service insertion, service monitoring, resiliency, and load balancing for security inspection services. This enables corporations to account for inspection-service availability when designing encrypted traffic flows and distributing traffic across supported services.
Flexible Inspection and Deployment
BIG-IP SSL Orchestrator supports exclusive inspection service types, consisting of inline Layer 2 and Layer 3 offerings, HTTP proxy services, ICAP offerings, and passive or receive-best inspection services. F5 additionally supports standalone, clustered, and separate ingress or egress deployment modes.
Benefits of BIG-IP SSL Orchestrator
BIG-IP SSL Orchestrator facilitates businesses in enhancing encrypted traffic visibility without requiring each security device to independently manage SSL/TLS decryption.
Key benefits include:
- Better visibility into encrypted traffic
- Reduced SSL/TLS inspection blind spots
- Centralized traffic orchestration
- Policy-based traffic steering
- Dynamic security service chaining
- More efficient use of existing inspection tools
- Improved security service availability
- Load balancing across supported services
- Greater control over protocols and ciphers
Deployment and Management Options
BIG-IP SSL Orchestrator is a software module deployed on the F5 BIG-IP platform. F5 documentation states that it can be provisioned on supported BIG-IP hardware appliances, VIPRION and VELOS chassis, and Virtual Edition.
Hardware Deployment
Organizations can set up SSL Orchestrator on supported F5 hardware systems for on-premises data centers and different dedicated infrastructure environments. The suitable platform depends on the organization’s traffic requirements, architecture, and supported functional necessities.
Virtual Edition
SSL Orchestrator can also be deployed through BIG-IP Virtual Edition. F5’s current product statistics identify virtual deployment on supported hypervisors and in AWS, Azure, and Google Cloud environments.
Deployment Topologies
SSL Orchestrator supports different traffic-handling architectures, which include transparent and explicit proxy modes. F5 additionally offers standalone, clustered, and separate ingress or egress deployment modes for different network designs.
Management and Automation
F5 provides Guided Configuration for configuring SSL Orchestrator and associated items. Organizations can also use F5’s Ansible collections to create BIG-IP objects and configure and set up SSL Orchestrator topologies via automation.
BIG-IP SSL Orchestrator Product Categories
Netmate IT can arrange BIG-IP SSL Orchestrator into the following solution categories to help clients apprehend in which it fits inside an corporation security architecture.
SSL/TLS Visibility and Inspection
Provides decryption and re-encryption of SSL/TLS traffic so supported security services can inspect encrypted traffic.
Security Service Chaining
Creates logical inspection paths that direct traffic through selected security services in line with defined rules.
Traffic Steering and Orchestration
Manages how encrypted traffic flows are handled via the security stack using policy-based traffic handling and contextual information.
Security Inspection Integration
Supports distinct protection inspection service types and integration with third-party protection technologies.
Recommended BIG-IP SSL Orchestrator Solutions
Different organizations require different SSL/TLS inspection architectures relying on traffic routes, security tools, and infrastructure.
Outbound SSL/TLS Inspection
For corporations that need visibility into encrypted traffic leaving their network, an outbound inspection architecture can decrypt relevant sessions and direct them through selected security services before traffic continues to its destination.
Inbound SSL/TLS Inspection
Organizations protecting internet-facing applications can use an inbound inspection architecture to inspect encrypted traffic before it reaches protected applications. The appropriate layout relies on the application delivery and reverse proxy structure.
Multi-Tool Security Inspection
Organizations the usage of numerous security inspection tools can use dynamic service chaining and policy-based traffic steering to decide which traffic needs to pass through particular services. This can reduce the need for manually configured inspection paths.
High-Availability Inspection
Organizations where security inspection availability is essential can lay out their architecture around service monitoring, resiliency, and load balancing capabilities supported through SSL Orchestrator.
Industries We Support
BIG-IP SSL Orchestrator may be relevant to organizations that handle sensitive data, run complex networks, or use multiple security inspection technologies. Netmate IT helps meet requirements throughout industries including:
- Banking and Financial Services
- Government Organizations
- Healthcare and Medical Facilities
- Education and Universities
- Retail and E-Commerce
- Manufacturing and Industrial Operations
- Telecommunications
- Logistics and Transportation
- Energy and Utilities
- Professional Services
- Data Centers
- Managed Service Providers
Real-World Use Cases
A corporation may additionally have security tools that cannot directly inspect encrypted outbound traffic. BIG-IP SSL Orchestrator can decrypt relevant traffic and direct it through selected protection inspection services, helping the organization gain visibility into outbound connections and potential malicious activity. F5 especially identifies outbound traffic visibility as a key use case.
An organization’s website hosting internet-facing applications may also need to inspect encrypted inbound traffic before it reaches protected applications. SSL Orchestrator can be integrated into the appropriate inbound traffic structure to make encrypted sessions available for security inspection.
Why Choose Netmate IT for BIG-IP SSL Orchestrator
Deploying SSL Orchestrator requires more than enabling SSL/TLS decryption. Organizations need to understand traffic flows, determine which traffic requires inspection, combine security services, configure regulations, and select a deployment architecture that suits their infrastructure.
Netmate IT allows companies to evaluate and install F5 solutions based on their networking and security requirements. Its services can include assessment, solution planning, implementation, integration with current security services, configuration, troubleshooting, optimization, maintenance, and ongoing technical assistance.
FAQs
1. What is BIG-IP SSL Orchestrator?
BIG-IP SSL Orchestrator is an F5 solution for decrypting, examining, and re-encrypting SSL/TLS traffic. It also affords traffic steering and dynamic provider chaining throughout security inspection offerings.
2. What does BIG-IP SSL Orchestrator do?
It makes encrypted traffic visible to supported security inspection offerings by handling SSL/TLS decryption and re-encryption. It can also decide how traffic flows through the security stack using rules and service chains.
3. Why is SSL/TLS inspection important?
Encryption protects information in transit, but it is able to prevent security tools from analyzing doubtlessly malicious content within encrypted traffic. SSL/TLS inspection gives the security team visibility into relevant encrypted traffic.
4. Can BIG-IP SSL Orchestrator inspect inbound and outbound traffic?
Yes. F5 identifies each inbound and outbound SSL/TLS traffic flow of BIG-IP SSL Orchestrator. The appropriate structure relies upon the agency’s traffic flows and network design.
5. Where can BIG-IP SSL Orchestrator be deployed?
F5 documentation states that SSL Orchestrator can be provisioned on supported BIG-IP hardware appliances, VIPRION and VELOS chassis, and Virtual Editions. F5 additionally identifies supported virtual deployments in data centers, colocation centers, and public cloud environments.
6. Can BIG-IP SSL Orchestrator integrate with security tools?
Yes. F5 defines SSL Orchestrator to be vendor- and product-agnostic and supports different inspection service types, including inline Layer 2 and Layer 3 services, HTTP proxy, ICAP, and passive or receive-only inspection services.

Reviews
There are no reviews yet.